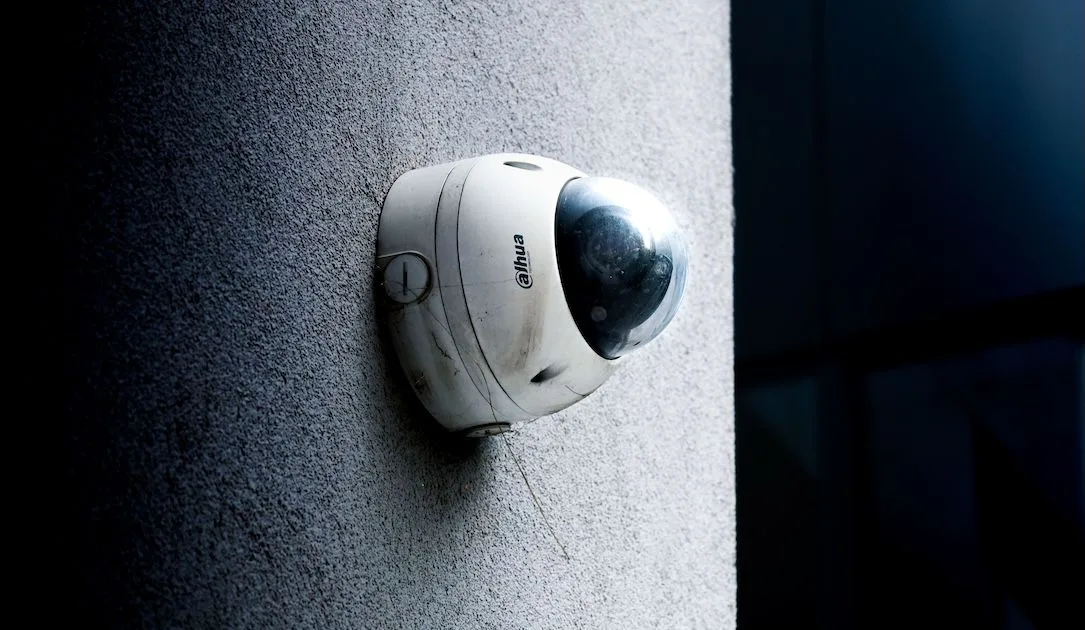
Researchers at Ukraine's computer emergency response team have raised alarms over unauthorized access to surveillance devices manufactured by Dahua, a major Chinese producer of video security systems. The intrusions have enabled threat actors to view live feeds, modify device configurations and establish illicit administrative accounts, according to CERT-UA's recent disclosure.
The vulnerability chain centers on a feature called Easy4IP, which facilitates remote camera access through Dahua's cloud infrastructure by linking devices via their serial numbers. This mechanism operates independently of conventional firewall protections or direct internet connectivity barriers. CERT-UA determined that the serial number scheme follows predictable sequences, permitting attackers to systematically enumerate and locate cameras connected to the cloud service without prior knowledge of specific device identifiers.
Following device discovery, adversaries exploit weak authentication credentials or security gaps in older firmware versions to establish control. CERT-UA specifically highlighted two critical flaws—CVE-2021-33044 and CVE-2021-33045—from 2021 that impact certain Dahua camera and recording systems.
Hunt.io researchers documented a separate campaign in August involving compromises of over 14,500 Dahua installations, with the majority concentrated across Ukrainian and Russian territories. The operational similarities suggest possible coordination, though definitive connections to CERT-UA's findings remain unconfirmed.
Dahua has faced sustained scrutiny from Western governments. The U.S. Congress barred federal procurement of certain Dahua products in 2018, and the following year the Trump administration designated the company as a trade-restricted entity due to alleged involvement in surveillance and suppression activities targeting Uyghurs and other Muslim populations in Xinjiang.
Wartime surveillance vulnerabilities
The disclosure arrives as Ukraine confronts persistent concerns that compromised cameras could serve Russian military intelligence operations. The SBU, Ukraine's domestic security agency, has identified and neutralized approximately 40,000 surveillance systems since Russia's 2022 invasion commenced, driven by fears of reconnaissance exploitation.
In January 2024, the SBU disclosed that Russian operatives had penetrated two cameras mounted on residential structures in Kyiv. The devices, originally positioned to observe street-level activity and parking zones, were repositioned by the attackers to monitor air defense installations and vital infrastructure, with footage reportedly streamed to YouTube.
A 2024 investigation by Radio Free Europe/Radio Liberty identified roughly 24,000 cameras from Dahua and Hikvision—another Chinese manufacturer—deployed across Ukrainian municipal surveillance networks. Government procurement filings demonstrate that Ukrainian state bodies and armed forces continued acquiring Dahua systems through 2026 despite documented security risks.
CERT-UA has not clarified whether the compromised devices identified in its alert include systems deployed by Ukrainian government agencies or military formations.