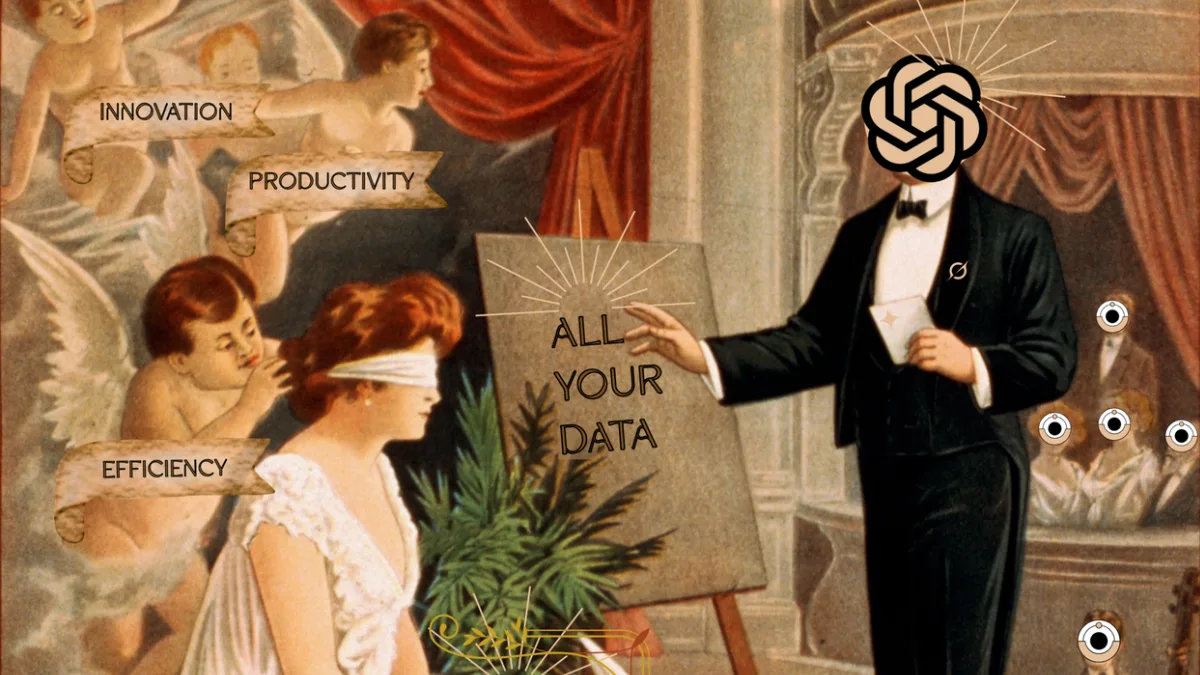
The internet's foundational business model rests on surveillance. Advertising revenues depend on personal data collection, which fuels the broader surveillance economy. Beyond ad targeting, this information serves multiple purposes: shaping social media experiences and powering AI training systems. Addressing industry's data practices is critical to tackling engineered addiction, algorithmic manipulation, and democratic erosion. The regulatory response to social media surveillance largely failed; the emergence of AI agents offers a narrowing window to pursue a different path. Establishing mandatory data minimization standards for AI agents has become imperative.
Nearly every internet-connected industrial system maximizes personal data collection. Users possess limited privacy levers through browsers, applications, and extensions. Technical safeguards like encryption and legal frameworks such as Europe's GDPR and California's CCPA create isolated privacy zones. However, the dominant pattern allows individuals to "consent" through cursory notice-and-click arrangements—a facade of choice masking the absence of genuine agency. Data maximization and surveillance capitalism prevail across most digital interactions.
AI agents replicate and amplify these privacy challenges. The financial incentive of advertising persists alongside demand for data to customize pricing and train subsequent AI systems. Companies will intensify existing surveillance tactics while marketing themselves as privacy-conscious. The industry has already signaled its intentions through products saturated with consumer information. Personalized chatbots deliver tailored recommendations and simulated companionship. Personal AI agents such as Instinct grant themselves access to user accounts, communications, keystroke logs, and interaction patterns.
AI agents introduce distinct privacy risks beyond conventional digital threats. They aspire to deeper integration than browsers, email, messaging platforms, or smartphones. Operating with autonomy and minimal supervision, they accumulate access to expansive personal datasets across multiple tasks and contexts over extended periods. They delegate work to other tools and agents without respecting organizational, institutional, or geographic boundaries—complicating oversight. They wield personal information as a tool for behavioral manipulation.
Governments must reverse course and embrace data minimization as the governing principle. Data minimization should function as a binding legal default, with narrow exceptions only when demonstrable, informed consent is established. This foundation underpins what researchers term Privacy Preference Controls for Agentic Systems. Surveillance capitalism and its associated data extraction are not prerequisites for innovation or service improvement. Contrary to claims that privacy holds no value or has already vanished, individuals demonstrate genuine privacy concerns. Although nuanced, privacy reasoning is learnable. Technically sound consent mechanisms exist; relying on superficial notice-and-click procedures lacks justification. Most critically, weaponizing personal information to influence behavior poses an escalating threat to individual autonomy and democratic institutions in an AI-saturated environment.
Data minimization extends beyond privacy protection into the domain of trust. It ensures agents execute only user-authorized functions within defined parameters, preventing unrestricted operation across undefined objectives without enforceable limits. Explicit authorization and task specification restrict agent scope and intensity. This "transactional friction" benefits conventional privacy interests while addressing broader concerns around cognitive security, safety, and accountability. Trustworthy AI systems cannot exist without data minimization requirements.
Enterprise customers already demand and obtain such protections through negotiation with software providers. Ordinary users deserve equivalent safeguards. Law firms, hospitals, and financial institutions substantially restrict personal data collection, processing, retention, and distribution when engaging with AI agents, while mandating explicit use cases, task boundaries, and authorization protocols. Consumers, by contrast, face pressure to grant personal AI agents unrestricted access and blanket operational authority—leaving them vulnerable when failures occur.
Data minimization strengthens security posture. As data theft and system breaches remain commonplace, limiting data collection reduces exposure by decreasing the number of locations where personal information exists. Deletion remains the most effective defense against malicious actors seeking to steal data.
Market forces will not generate these protections. Companies built on surveillance capitalism will pursue data maximization while issuing contradictory marketing claims. Technology firms seek unlimited agent task scope: permitting software to manage every aspect of life, including functions users never requested or recognized as requiring automation. The familiar appeal emphasizes convenience through total outsourcing of human judgment.
Despite industry assertions, maximized surveillance is neither inevitable nor beneficial for AI agents. Governments retain the capacity to enact stringent privacy rules centered on data minimization, though action cannot be delayed indefinitely.
Societies must establish a strict, legally binding data minimization requirement for AI agents. Companies should collect and process only information demonstrably necessary for user-specified and authorized functions. Combined with appropriate privacy controls, this approach enables AI agents that genuinely respect user preferences across both conventional web and agentic environments.