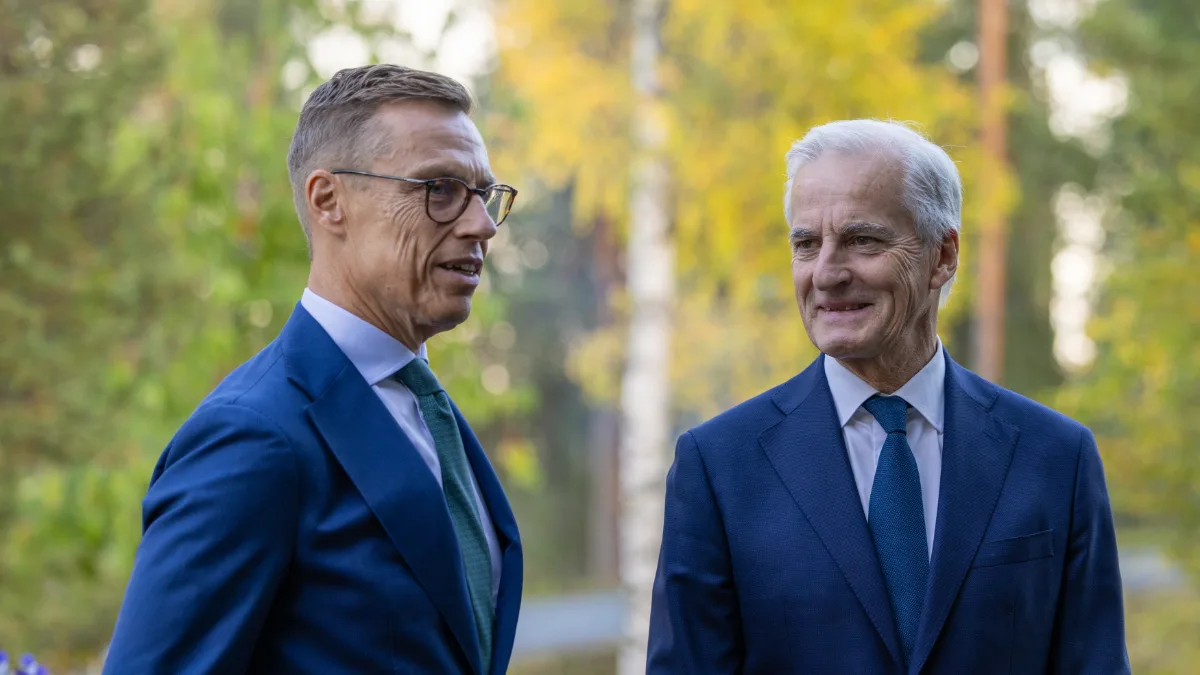
Last month, executives and officials representing a coalition of more than 30 nations, predominantly from Europe, endorsed a statement initiated by Finland's president and Norway's prime minister. The call demands tighter governance of frontier AI systems, including compulsory testing before deployment, independent assessment mechanisms, unified technical standards, mandatory incident disclosure, access to scientific resources and credible evaluation frameworks. The statement also suggests investigating whether a new international body should be created to establish norms, enable verification and coordinate action when technological capabilities reach critical levels. While the first set of proposals merits serious consideration, the second warrants deeper examination.
The underlying problem is clear: few organizations possess the technical expertise to independently assess, examine and scrutinize cutting-edge AI systems. Simultaneously, a handful of firms command most of the computational resources, financial backing, technical talent and proprietary access to the most sophisticated models. This dynamic puts governments in a precarious position—they may become reliant on the very companies they aim to oversee for the technical evidence required to do so.
The solution lies in building technical capacity incrementally from the ground level upward.
The Internet's Distributed Model
The Internet offers a valuable historical precedent. Its worldwide expansion developed alongside a framework of distributed rather than centralized governance. No single institution wielded authority over the entire network. Instead, distinct organizations managed specific responsibilities and maintained connections through shared technical specifications, communication protocols and coordination structures. The Internet Engineering Task Force (IETF) created the technical standards enabling disparate networks and platforms to function together. The Regional Internet Registries managed Internet address allocations within geographic regions. The Internet Corporation for Assigned Names and Numbers (ICANN) oversaw essential naming systems while collaborating with technical specialists and regional bodies. Crucially, none of these entities controlled the Internet itself. Their mandates were circumscribed, and their success stemmed partly from operating within a broader framework of dispersed technical authority.
This organizational structure did not emerge from a single master plan handed down from above; rather, it developed organically as the network itself matured. Emerging challenges prompted the creation of fresh institutions, methodologies and coordination frameworks; established bodies evolved to meet new demands; and specialized knowledge remained spread across many actors. While this arrangement did not eliminate disagreement or political tension, it prevented the governance of a planetary network from becoming concentrated in a single locus of power or knowledge.
Lessons from Internet Security
Internet security history reinforces this principle. When the Morris worm struck in 1988, causing widespread disruption across the Internet, the initial reaction lacked coordination and coherence. Though the CERT Coordination Center was founded, it did not evolve into a worldwide cybersecurity command center. Rather, specialized response units emerged across different infrastructure segments, industries and nations. The establishment of the Forum of Incident Response and Security Teams, or FIRST, in 1990 created a framework for these units to share findings and work together across geographic boundaries. The underlying logic was straightforward: cultivate technical expertise in proximity to where issues materialize, then link those capabilities together.
This strategy proved vital because a security breach affecting one network can cascade to many others. A flaw identified in one system may compromise thousands more. Rather than funneling every incident through a single institution, the approach ensured that numerous organizations could spot, examine and handle problems while maintaining channels to disseminate their discoveries. Today, FIRST unites incident-response personnel from state agencies, private enterprises and universities, operating on precisely this principle.
Applying the Model to AI
The takeaway for AI governance is not to replicate the IETF, ICANN or CERT structures wholesale. AI operates as a fundamentally distinct technology with a far more consolidated architecture. The applicable lesson is structural: when a worldwide system grows too intricate and fragmented to be managed from a single point, establish expertise where it is most needed and link it via shared procedures.
AI currently faces nearly the inverse situation. Its technical foundation remains tightly concentrated, whereas independent governance expertise remains underdeveloped. This is where the growing ecosystem of AI safety, security and evaluation centers becomes significant. These organizations can furnish the analytical capacity governments require: conducting assessments of models, gauging potential harms, examining security events, creating evaluation metrics and questioning vendor assertions. Through international partnerships, their contributions can become standardized and valuable across borders.
Not every nation requires its own frontier-model testing facility. However, countries should be able to cultivate competencies suited to how AI will function in their particular circumstances. A specialist in Nairobi may detect hazards connected to linguistic variation or government applications that a reviewer in Silicon Valley overlooks. An organization in New Delhi may grasp implementation realities that remain invisible to a European assessment center. A domestic or regional assessment facility can evaluate not merely whether a system functions safely in principle, but whether it suits the governance structures, populations and infrastructure where deployment will occur.
Digital Sovereignty Redefined
This perspective also addresses arguments surrounding digital sovereignty. In the current technological landscape, digital sovereignty should not revolve exclusively around technological independence or manufacturing all components locally. It should instead encompass the power to shape how AI operates within a nation's legal, financial and societal frameworks; to recognize its prospective gains and dangers; and to make deliberate choices about acceptable hazards.
Achieving this demands specialized knowledge. A government cannot meaningfully decide how to deploy AI if it depends entirely on the firms constructing it or on evaluations conducted elsewhere. Rather than concentrating expertise in one place, the answer is to spread it widely and ensure it functions together. An assessment performed in London ought to align with one executed in Nairobi. A testing framework created in Singapore ought to be applicable elsewhere. A security flaw uncovered in one location should not remain isolated. Techniques, findings, security reports and insights should traverse international lines.
This necessitates unified benchmarks for assessment, cybersecurity, information management and disclosure; dependable pathways for exchanging classified material; certification frameworks allowing organizations to demonstrate their technical and security readiness for frontier systems; and regulated pathways to model availability. A multistakeholder governance structure can strengthen AI oversight by bringing together the varied competencies needed to examine, comprehend and oversee these innovations.
States can establish regulations and accountability mechanisms; technology firms can grant access and share technical specifics; scholars and autonomous centers can examine and contest systems; and advocacy groups can contribute insights on freedoms, adverse effects and practical consequences. The aim is not to grant every participant equivalent authority, but to guarantee that no single party monopolizes the information required to govern AI.
Building the Network
The expanding network of AI safety and evaluation centers therefore constitutes a vital component of this framework. It delivers something a solitary worldwide authority cannot furnish independently: autonomous technical expertise positioned where it is required. Governments maintain a crucial function in mandating evaluation, assessment, confirmation, disclosure and early notification requirements, plus establishing specifications for availability, protection and responsibility. They should likewise allocate resources to domestic and regional competencies. Yet they need not monopolize that expertise. Worldwide bodies can articulate shared benchmarks and facilitate diplomatic engagement, while autonomous centers deliver the technical means to confirm whether those benchmarks are being satisfied. The vision should be a framework in which knowledge is dispersed, coordinated and equipped to hold both governments and corporations accountable.
The focus must be on reinforcing the institutional network capable of implementing these requirements: centers that can autonomously examine AI wherever necessary, and frameworks enabling their findings to be transmitted globally.
The Internet did not become manageable because authorities eventually identified the appropriate institution to oversee it. It became manageable because technical duties were distributed and those responsible for them mastered collaboration. AI governance must embrace that identical principle.