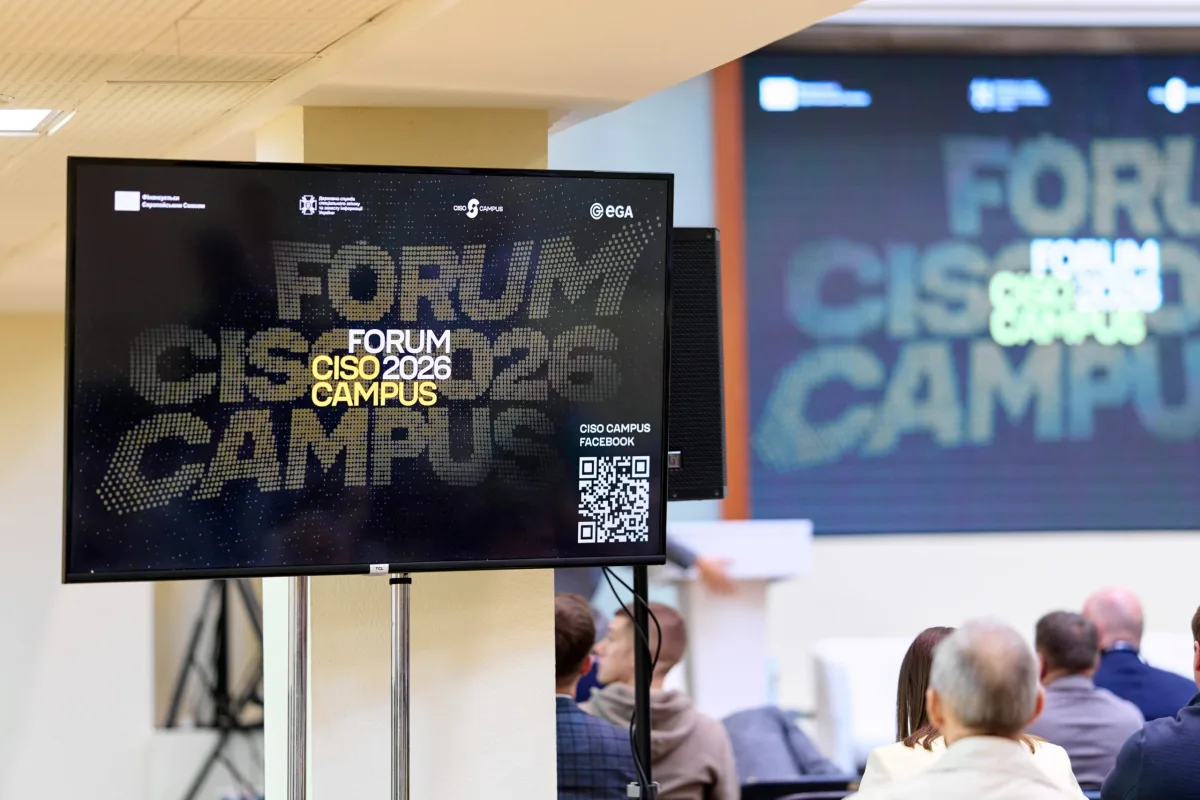
The State Service of Special Communications and Information Protection of Ukraine (SSSCIP) and the e-Governance Academy (eGA) convened cybersecurity leaders from government, military, business and international organisations at the inaugural CISO Forum in Kyiv on 2 October. The event, backed by the EU-funded Continued EU Support to Cybersecurity initiative (EU4CyberUA), aimed to strengthen the Chief Information Security Officer position in Ukraine and chart practical pathways for advancing cybersecurity governance and cross-sector collaboration.
Ukraine embedded the CISO role into its legal framework in 2025, a significant institutional milestone. However, translating legislation into operational reality demands qualified personnel, transparent organisational positioning of the role, practical implementation resources, and a functioning professional network for knowledge-sharing among practitioners.
The Forum examined how CISOs operate on the ground. Participants from central government bodies, regional military structures, commercial enterprises, EU partners and subject-matter experts convened to surface current obstacles and map the trajectory for the role's evolution within Ukraine.
CISOs and their teams must adopt a systematic approach to cybersecurity: assessing risks, setting priorities, and ensuring organisational readiness for cyber incidents. To achieve this, a cybersecurity lead must possess the necessary expertise and sufficient authority to act. Our mission is to foster an environment where this role genuinely bolsters the cyber resilience of government agencies and other organisations. A critical factor in reaching this goal is building a robust professional community and maintaining a constant, effective dialogue between those who set the regulations and those who implement them. The CISO Forum should serve as a key platform, bringing us all together annually to exchange insights.
Volodymyr Trofymenko, Deputy Chairman of SSSCIP
The emergence of the CISO function signals a fundamental reorientation in cybersecurity strategy, moving away from reactive technical incident management towards proactive, organisation-wide cyber risk governance. This paradigm demands explicit accountability structures, embedding security considerations into corporate decision-making, and treating cyber exposure as a strategic concern. Through this shift, Ukraine is converging with established European cybersecurity governance models.
Strong cyber risk management is an integral part of the resilience of a modern state. The European Union supports Ukraine not only in strengthening its technical capabilities, but also in developing professional expertise and effective cybersecurity governance. The development of the CISO role is an important part of this work
Asier Santillan Luzuriaga, Head of Section at the Delegation of the European Union to Ukraine
Parallel to formalising the CISO position, Ukraine is establishing infrastructure for continuous professional development of cybersecurity leaders. CISO Campus delivers training in management and professional competencies for the role, merging classroom instruction with real-world case studies and practitioner experience. The Forum extended this capacity-building effort by convening the professional community and facilitating peer-to-peer learning. Expanding CISO Campus further will require broadening training availability to reach additional CISOs throughout the country.
We are seeing strong demand for professional CISO training, and the next step is to make it available to more specialists. This requires additional expertise, people and resources. With Ukraine at war and public resources focused on critical priorities, support from international partners is particularly important for the continued development of CISO Campus and for expanding training opportunities.
Ieva Ilves, CEO of CISO Campus
Workshop sessions tackled operational challenges confronting CISOs in their daily responsibilities: managing cyber incident response, coordinating with CERT-UA, building regional cyber resilience infrastructure, and safeguarding state information systems. These topics carry heightened urgency for Ukraine, where CISOs operate within an active military conflict and cyber defence directly underpins the functioning of essential infrastructure and public services.
Ukraine has already accumulated exceptionally valuable experience in countering cyber threats under real-world conditions. Through EU4CyberUA, eGA experts can build on this experience by sharing international best practices, practical tools and new opportunities for the professional development of CISOs. Bringing these elements together strengthens both cybersecurity professionals and the organisations they protect.
Taimar Peterkop, Project Team Leader of EU4CyberUA at eGA
A second day of programming, designated CSIRT Day, extended the professional dialogue with emphasis on the regional dimension of cybersecurity. Attendees examined the establishment of regional cybersecurity centres, their coordination with CERT-UA, and the role of regional teams in delivering services at the national scale.
The inaugural CISO Forum represents a transition point: from embedding the CISO role in statutory language to operationalising it across organisations and cultivating a cohesive professional community of cybersecurity leaders in Ukraine.
The Forum was organised under the EU-funded Continued EU Support to Cybersecurity programme (EU4CyberUA), which runs from 2026 to 2029 with a budget of €10 million. The initiative assists Ukraine in reinforcing national cyber resilience and harmonising with European cybersecurity standards. Implementation is carried out by FIAP and eGA in partnership with SSSCIP.