The cybersecurity domain underwent a fundamental shift in March 2026 when Anthropic and OpenAI released AI models capable of identifying vulnerabilities in digital infrastructure, distributing them exclusively to vetted partners. This acceleration has transformed the nature of cyber conflict, upending earlier expectations about gradual AI advancement.
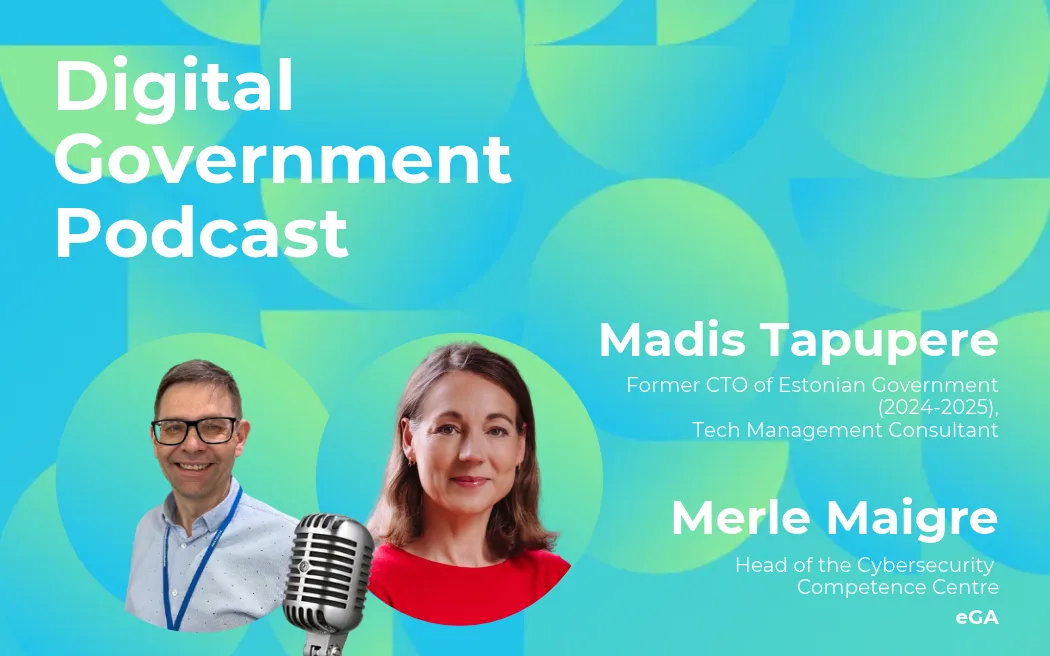
Madis Tapupere, who previously served as CTO of the Estonian Government and now works as a Tech Management Consultant, joined colleagues from government, industry and academia in responding to a pressing challenge: if offensive cyber capabilities were becoming radically cheaper and more accessible, how should nations prepare? Their answer became National Cyber Resilience in the Age of AI: A Doctrine for Asymmetric Cyber Defence, a white paper examined in a discussion hosted by Merle Maigre, Head of Cybersecurity at the e-Governance Academy.
Tapupere observes that "A lot of stuff that has been kind of preached so far has just become more relevant. We need to do a lot of things we have been talking about for years – just much better, now."
What the state cannot afford to lose
The white paper identifies a troubling acceleration in how quickly vulnerabilities move from discovery to exploitation. In 2018, the typical window between public disclosure and active exploitation was approximately two years. By 2023, this had compressed to five days. In 2026, adversaries sometimes weaponise flaws before official disclosure occurs. Work that once demanded months of specialist effort from elite teams can now be completed in hours by a much broader pool of actors—extending far beyond the state intelligence agencies that historically monopolised sophisticated cyberattacks. The paper proposes six policy responses to this transformed environment.
The initial two recommendations address prioritisation and protection strategy. Attempting to defend all systems with equal rigour inevitably leaves all systems inadequately protected. The first recommendation calls for identifying a narrow range of essential functions—identity verification, financial systems, emergency response, governmental continuity—that cannot tolerate even brief outages, and applying the highest security standards exclusively to these. The paper terms this concept the Minimum Viable State. However, much of this critical infrastructure operates under private sector control rather than government ownership.
When pressed on the resulting friction between public security requirements and private sector autonomy, Tapupere draws on Estonia's experience navigating this tension through data-embassy initiatives and his tenure as CTO. He acknowledges that "It's never a joyful thing for a private sector company to be loaded with additional regulatory pressure," yet maintains that "it seems to be working as a system."
The second recommendation flows logically from the first: establishing a National Trust Backbone. This comprises an interconnected system of dependable public and private components—identity services, digital signatures, registries, data exchange, audit functions, hosting infrastructure—ensuring that all government operations maintain full legal validity and trustworthiness. Yet concentrating critical functions creates an inviting target: compromising the system upon which everyone depends yields enormous returns. Tapupere's response is direct: "You don't avoid it. You can just address the protection better."
His solution emphasises redundancy rather than retreat. Estonia's existing infrastructure already distributes functions across multiple locations rather than concentrating them in a single facility, a principle the doctrine formalises. The 2017 discovery of a vulnerability in chips used in approximately 750,000 Estonian ID cards illustrates this approach. The flaw prompted a precautionary suspension of certificates, yet the nation continued functioning normally because it had never depended on any single authentication method.
The necessity to keep up pace with machine-speed attacks
The remaining recommendations in the doctrine address the threat itself: how AI fundamentally alters attack patterns and the speed defenders must achieve. Tapupere explains that "AI is a tool – it speeds up vulnerability detection, but it also provides automation to the attackers." Capabilities once confined to a small number of nation-state teams have become "very democratised, available to almost anyone, not just sophisticated adversaries." Drawing from his background in internet banking security, Tapupere recalls investigating a fraud campaign that traced back to two twelve-year-olds struggling academically, equipped only with scripts obtained online—a harbinger of this democratisation.
Maigre contributes a parallel observation from British law enforcement: the acronym APT, traditionally denoting Advanced Persistent Threat and associated with sustained, well-resourced intrusions by nation-state intelligence, now humorously stands for Advanced Persistent Teenager. While the rebranding carries humour, the underlying transformation is serious. Operations requiring state backing and months of preparation a decade ago can now be executed by teenagers using downloaded tools—before considering how generative AI has further reduced barriers to entry.
If attack velocity has increased, defensive velocity must match. The doctrine's AI component rests on the premise that while attackers leverage AI to reduce costs and expand operational scale, the economics of cyber conflict should shift toward defenders. Monthly or even weekly software updates sufficed when attackers required months to weaponise flaws. This timeline no longer applies when exploitation can occur within hours. Tapupere argues that "This ability to make sense fast, react fast, decide fast, and patch fast needs to be on the defender side." When Maigre challenges whether AI-enabled defence can rebalance this asymmetry if attackers can deploy AI without regulatory constraints, accountability measures, concerns about false positives or service disruption, Tapupere identifies several ways automation can strengthen defensive capabilities.
First? Telling the truth
Beneath the technical arguments lies a deeper strategic concern to which Tapupere repeatedly returns. Hostile campaigns targeting democracies rarely seek to destroy infrastructure directly. Their genuine objective, the paper contends, is undermining citizen confidence in government function—a lesson Estonia learned through the 2007 attacks that established the nation as a cyber frontline. The white paper frames the stakes starkly: such campaigns aim to "make a country look broken to its own citizens, and the government slower than the news cycle in answering for it."
This reality demands disclosure preceding containment: pre-drafted incident response templates rehearsed before crises occur, ensuring the government's narrative reaches citizens before speculation takes hold. The paper cites Sweden's Psychological Defence Agency and Taiwan's practice of issuing signed government rebuttals within roughly an hour of false claims.
Maigre poses the question: "Should Estonia's cybersecurity authority start measuring itself by public confidence, rather than recovery times alone?" Tapupere expresses doubt that trust can be reduced to a single metric.
He contends that every individual within the cybersecurity authority must regard themselves as stewards of public trust, though no single agency can accomplish this alone. In Estonia, population registries fall under the Ministry of Internal Affairs, business registries under separate ministries, each bearing responsibility for its own data protection. The private sector similarly holds sensitive citizen information.
The implication is that cyber resilience transcends any single agency's responsibility but rather constitutes a shared obligation spanning every registry, every ministry and every organisation handling citizen data. Tapupere observes that "Whenever our digital government fails in some corner, the trust starts eroding."
Looking ahead five years, Tapupere sees AI's development mirroring the early internet era: constructed rapidly, then secured only after dangers became undeniable. He concludes that "I think we need to run very fast to stand still. If things won't have gone significantly worse, then we are already in a very good place." While hardly optimistic, this perspective offers a serious and substantive roadmap for the coming years.